BeyondTrust puts guardrails around the rise of Agentic AI
“What we find is that most organizations haven't even matured enough to develop the policies and procedures to get there,” says Morey J. Haber, Chief Security Advisor at BeyondTrust.
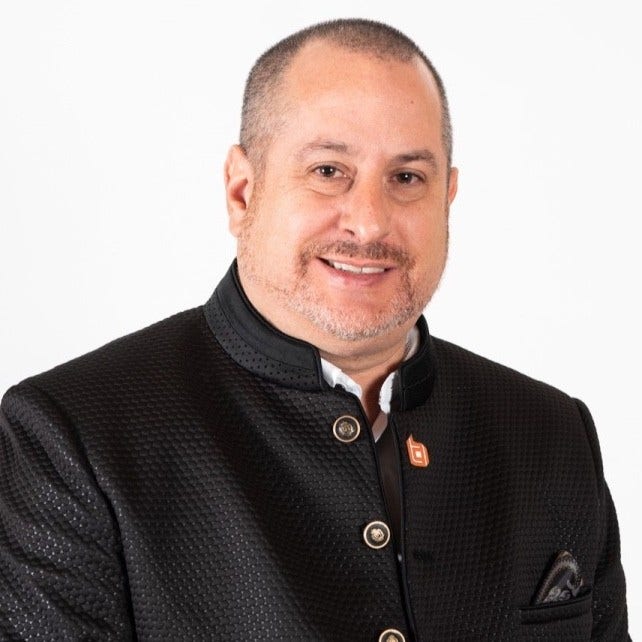
With guardrails becoming increasingly important for organizations when they deploy AI, Beyond Trust has some of the largest endpoint privilege management deployments in the world.
Recognized as a Leader in the 2026 Gartner Magic Quadrant for Privileged Access Management for the eighth consecutive edition of the report, BeyondTrust is positioned highest of all vendors in its Ability to Execute.
For Morey J. Haber, Chief Security Advisor at BeyondTrust, as the leading vendor in applying guardrails to AI, BeyondTrust also has some of the largest endpoint privilege management deployments in the world.
“What this allows us to do is look at all of those and enumerate, or basically log, because immutable logs are very important in agentic AI. We then built a library of guardrails with our Phantom Labs team,” Haber said.
As BeyondTrust's research team, Phantom Labs has developed a library of the 50 most common guardrails that organizations need.
“Everything from not trusting certain providers to blocking the enumeration of AI in the cloud. So, our research team has picked the most popular and high-risk items and ship it as a part of the product. Customers can test whether it applies to them and then apply it. For existing BeyondTrust customers, this is an easy add-on. For new customers, they get the benefit of least privilege, application control, and AI as well, all in one platform,” he said.
Findings from endpoint telemetry from BeyondTrust’s Phantom Labs research have revealed that AI coding agents requested approximately 1.28 million shell commands from 132,000 prompts. This is about 10 commands per prompt, demonstrating how a single prompt can translate into multiple downstream command requests.
Phantom Labs research also revealed that 85% of observed coding-agent users had MCP server connections, averaging 4.35 unique servers per connected user, with one user connected to 36. These connections extend an agent’s reach, potentially allowing it to act across multiple platforms with delegated use access.
Apart from that, the research also revealed that increasing agent skills on coding agents, especially in mid-market enterprise environments, not only influences prompt input and output, but also often contains embedded code. As adversaries actively distribute and poison legitimate skills, organizations without the ability to audit and enforce skill policy may be ceding unknown controlovero unapproved and/or compromised skills.
Having visibility
Non-human identities are increasing, and organizations need more tools to manage them. A lot of organizations are also realizing that with the introduction of more AI agents, the identities associated with these agents are just as risky as non-human identities.
For Haber, organizations need to first consider what they’re doing in terms of application control as a standard discipline.
“What we find is that most organizations haven't even matured enough to develop policies and procedures to get there. The technology exists to govern it, but what does your organization actually accept? And since they haven't gotten to that point yet, we see the rampant usage of AI,” he said.
According to Haber, BeyondTrust’s Identity Visibility and Intelligence Platform (IVIP) is the intelligence layer that tells organizations not just “who” has access, but what they can actually do with it.
“IVIP fills the gap in identity and access management by talking to SSO, MFA, PAM, IGA, IDP, and enumerates all of the identities, humans, non-humans, and machines, including AI and provides visibility and intelligence. How are they being used? What is it talking to? What data is being transmitted?” he said.
While IVIP provides visibility, Haber explained that there is still a need for organizations to have guardrails.
“How do you do it? This is where AI Agent Security comes in. It's an extension to our endpoint privilege management that actually allows you to put guardrails on those AI. So once a policy and procedure is implemented, you can now effectively make that work on the endpoint, more than just blocking a browser from running,” he explained.
Specifically, AI Agent Security applies BeyondTrust’s Visibility, Intelligence, and Protection framework to agentic AI on the endpoint, giving security teams the context and control to govern AI agents without limiting the access employees need to do their jobs.
Rather than relying solely on blocking known commands or detecting risky behavior after it occurs, BeyondTrust evaluates individual AI agent actions against policy at runtime to determine what an AI agent is permitted to do before an action is taken.