Kyndryl: Enterprises must fix security gaps before embracing AI
Kevin O'Leary, Head of Security & Resiliency at Kyndryl, wants organizations to understand that AI is not going to fix gaps in policies and procedures when implementing the technology.
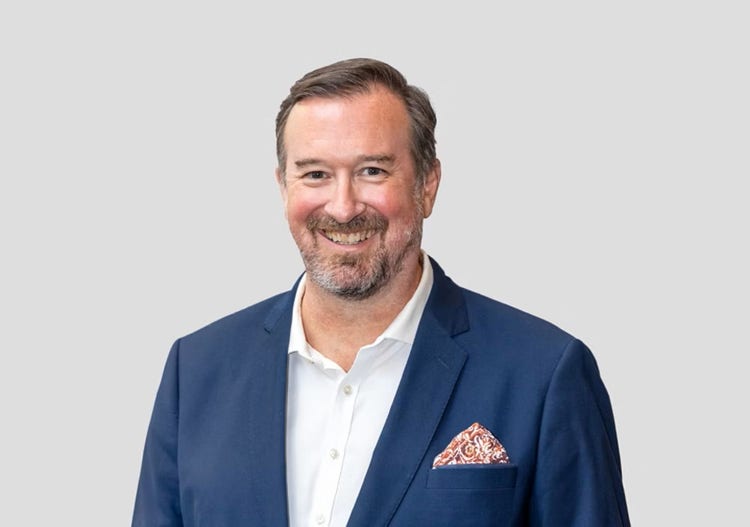
When it comes to using AI, Kevin O'Leary, Head of Security & Resiliency at Kyndryl believes that one of the mistakes organizations continue to make is the lack of having sufficient policies and procedures in place when using the technology.
In a conversation with CRN Asia, O’Leary explained that organizations can’t expect AI to create these for them because every company has its own specific issues and tech stack that it operates.
“You have to actually have that in place beforehand. You need to have your governance model, GRC, risk compliance, and all of that exist before you start layering AI into it and on top of it to improve it. But some companies, and especially in the region, unfortunately, have huge gaps in terms of their operational organization, especially on how they've documented and have managed change within the environment,” O’Leary said.
[Related: Kyndryl: APAC enterprises must close modernization gap as agentic AI accelerates]
He added that a lot of organizations in the region still have outdated documentation and data. The problem with this is that the AI tools implemented will come in and read data and give output from that data.
“AI is not going to create something for you from that perspective. It might see gaps; it might see holes, but it's not going to create that without the intervention of humans. And I think that a lot of tokens have been burnt to find problems that the human has then come in to fix before AI can come in and improve. So, that's a big issue,” he explained.
Another area is data sovereignty. O’Leary explained that the data sovereignty question is one that everyone has had to deal with in cybersecurity for a long time, especially with cloud in terms of where tenants are located and whether they're actually managing data within a specific region.
“I see the whole AI subject to be the same thing. How is it accessed? Where does the data actually move to, etc. So, some of it almost becomes a philosophical question in terms of data flows. So, if an AI model can access data, is it then moving the data to where it's location or is it just reading it and operating on it and leaving the data where it is? It's a little bit of a philosophical question. I think some countries are also starting to develop their own models to call it truly sovereign AI,” he added.
O’Leary also shared that Kyndryl has deployed more AI and agentic AI into its own internal SOC to not only protect Kyndryl but also offer as a service to customers.
“AI is absolutely a huge part of what we're operating within Kyndryl. But again, we have a lot of guardrails on that as well, and protections in terms of customer data and our own data as well. So, I see that in terms of how we are developing our SOC model, just to protect our own company is something that we can provide to customers as well,” he said.
Working with partners
In terms of partners that Kyndryl works with for cybersecurity, O’Leary said that every partner has AI embedded somewhere in their technology today.
“They have to, because it's expected, right? I think it's really about looking and saying, what's the right application of it within an environment. And partners see that a lot with the enterprise tools in terms of where have they placed it within the environment? What is the output from it? We can help in terms of the training of those models. And there's a big kind of a feedback loop between us and our partners in terms of providing the feedback and what customers are saying to us and how they then develop that in terms of their roadmap,” O’Leary explained.
He also stated that partners would need to look at what their entire roadmap is. The ones that stay stuck and don't actually move with the times are the ones that customers wouldn't work with while the ones that are pushing to the edges are the ones that customers are most looking at.
“It's for us to determine the best ones for the right situation,” he added.
Future of AI and cybersecurity
Looking ahead, O’Leary believes that there is no doubt that organizations are going to see a lot more pressure, especially with frontier models. This means, the pressure will be on organizations on how they respond to it at the moment.
“We were told that with Mythos AI, there would be a surge in patching that would be required. Now, that surge hasn't happened. But the reason it hasn't happened is because companies have asked Anthropic not to release it. There's usually a 90-day window where they have to release the vulnerabilities, so people are aware of it. So, they're asked to slow down. And that's what's been happening. So, it's been coming out more as a trickle,” he said.
For O’Leary, even that trickle is still a river compared to what came before.
“I think that the ability to respond is going to be extremely difficult for organizations, particularly in healthcare and in finance, where they have very small patching windows. So, you might only have four hours in a month or a quarter where you actually have patching. And what's happening is that most organizations have a long tail of vulnerabilities that they've never dealt with because they always do the critical first. So, they're always going down the list. Generally, those are medium to low, mostly low vulnerabilities, low-impact vulnerabilities,” he added.
At the same time, with the advent of AI and frontier AI models, O’Leary pointed out that there is going to be higher and more critical patches that are just not going to be dealt with.
“That means companies are exposed. It is not only a patching problem, but it's actually a reaction model as well,” he said.
This is also where O’Leary foresees virtual patching becoming even more important as it provides the capability to adjust the technology stack and the controls within it at the moment.
“And that's also where this idea of pushing zero trust and resilient by design will see more companies able to recover from attacks. They can build their resiliency to minimum viable company levels, especially on what they can operate or even sometimes go back to manual processes. These are all planning stages that people have to do,” he said.
He added that organizations are only going to see more of this in the future.
“AI isn't so much about discovering zero-day vulnerabilities, because there hasn't been a huge amount of that. But what AI has been very good at is chaining vulnerabilities that haven't been chained before. It is taking things that were low-level and chaining them in a way that actually provided the ability for higher-level vulnerabilities to be exploited,” O’Leary explained.
He believes that these are the things that are going to increase over time. And with cybersecurity being like an arms race, it will never end as every time vulnerabilities are fixed, the new one comes along.
“So, we're always piling them on top of each other. We're just mitigating what was in the past. The pile is getting higher and it's going to get even higher still,” he concluded.